Projects · 02
aws-platform-terraform
A production-style AWS platform in Terraform, built as reusable modules with tests, one roadmap item at a time.
Right now
Checking…
-
AWS platform checking
Open them directly: AWS platform
- My part
- It is how I am learning AWS platform engineering. A scheduled Claude Code run builds the next roadmap item and writes a note explaining it; I review each change and study the note.
- Result
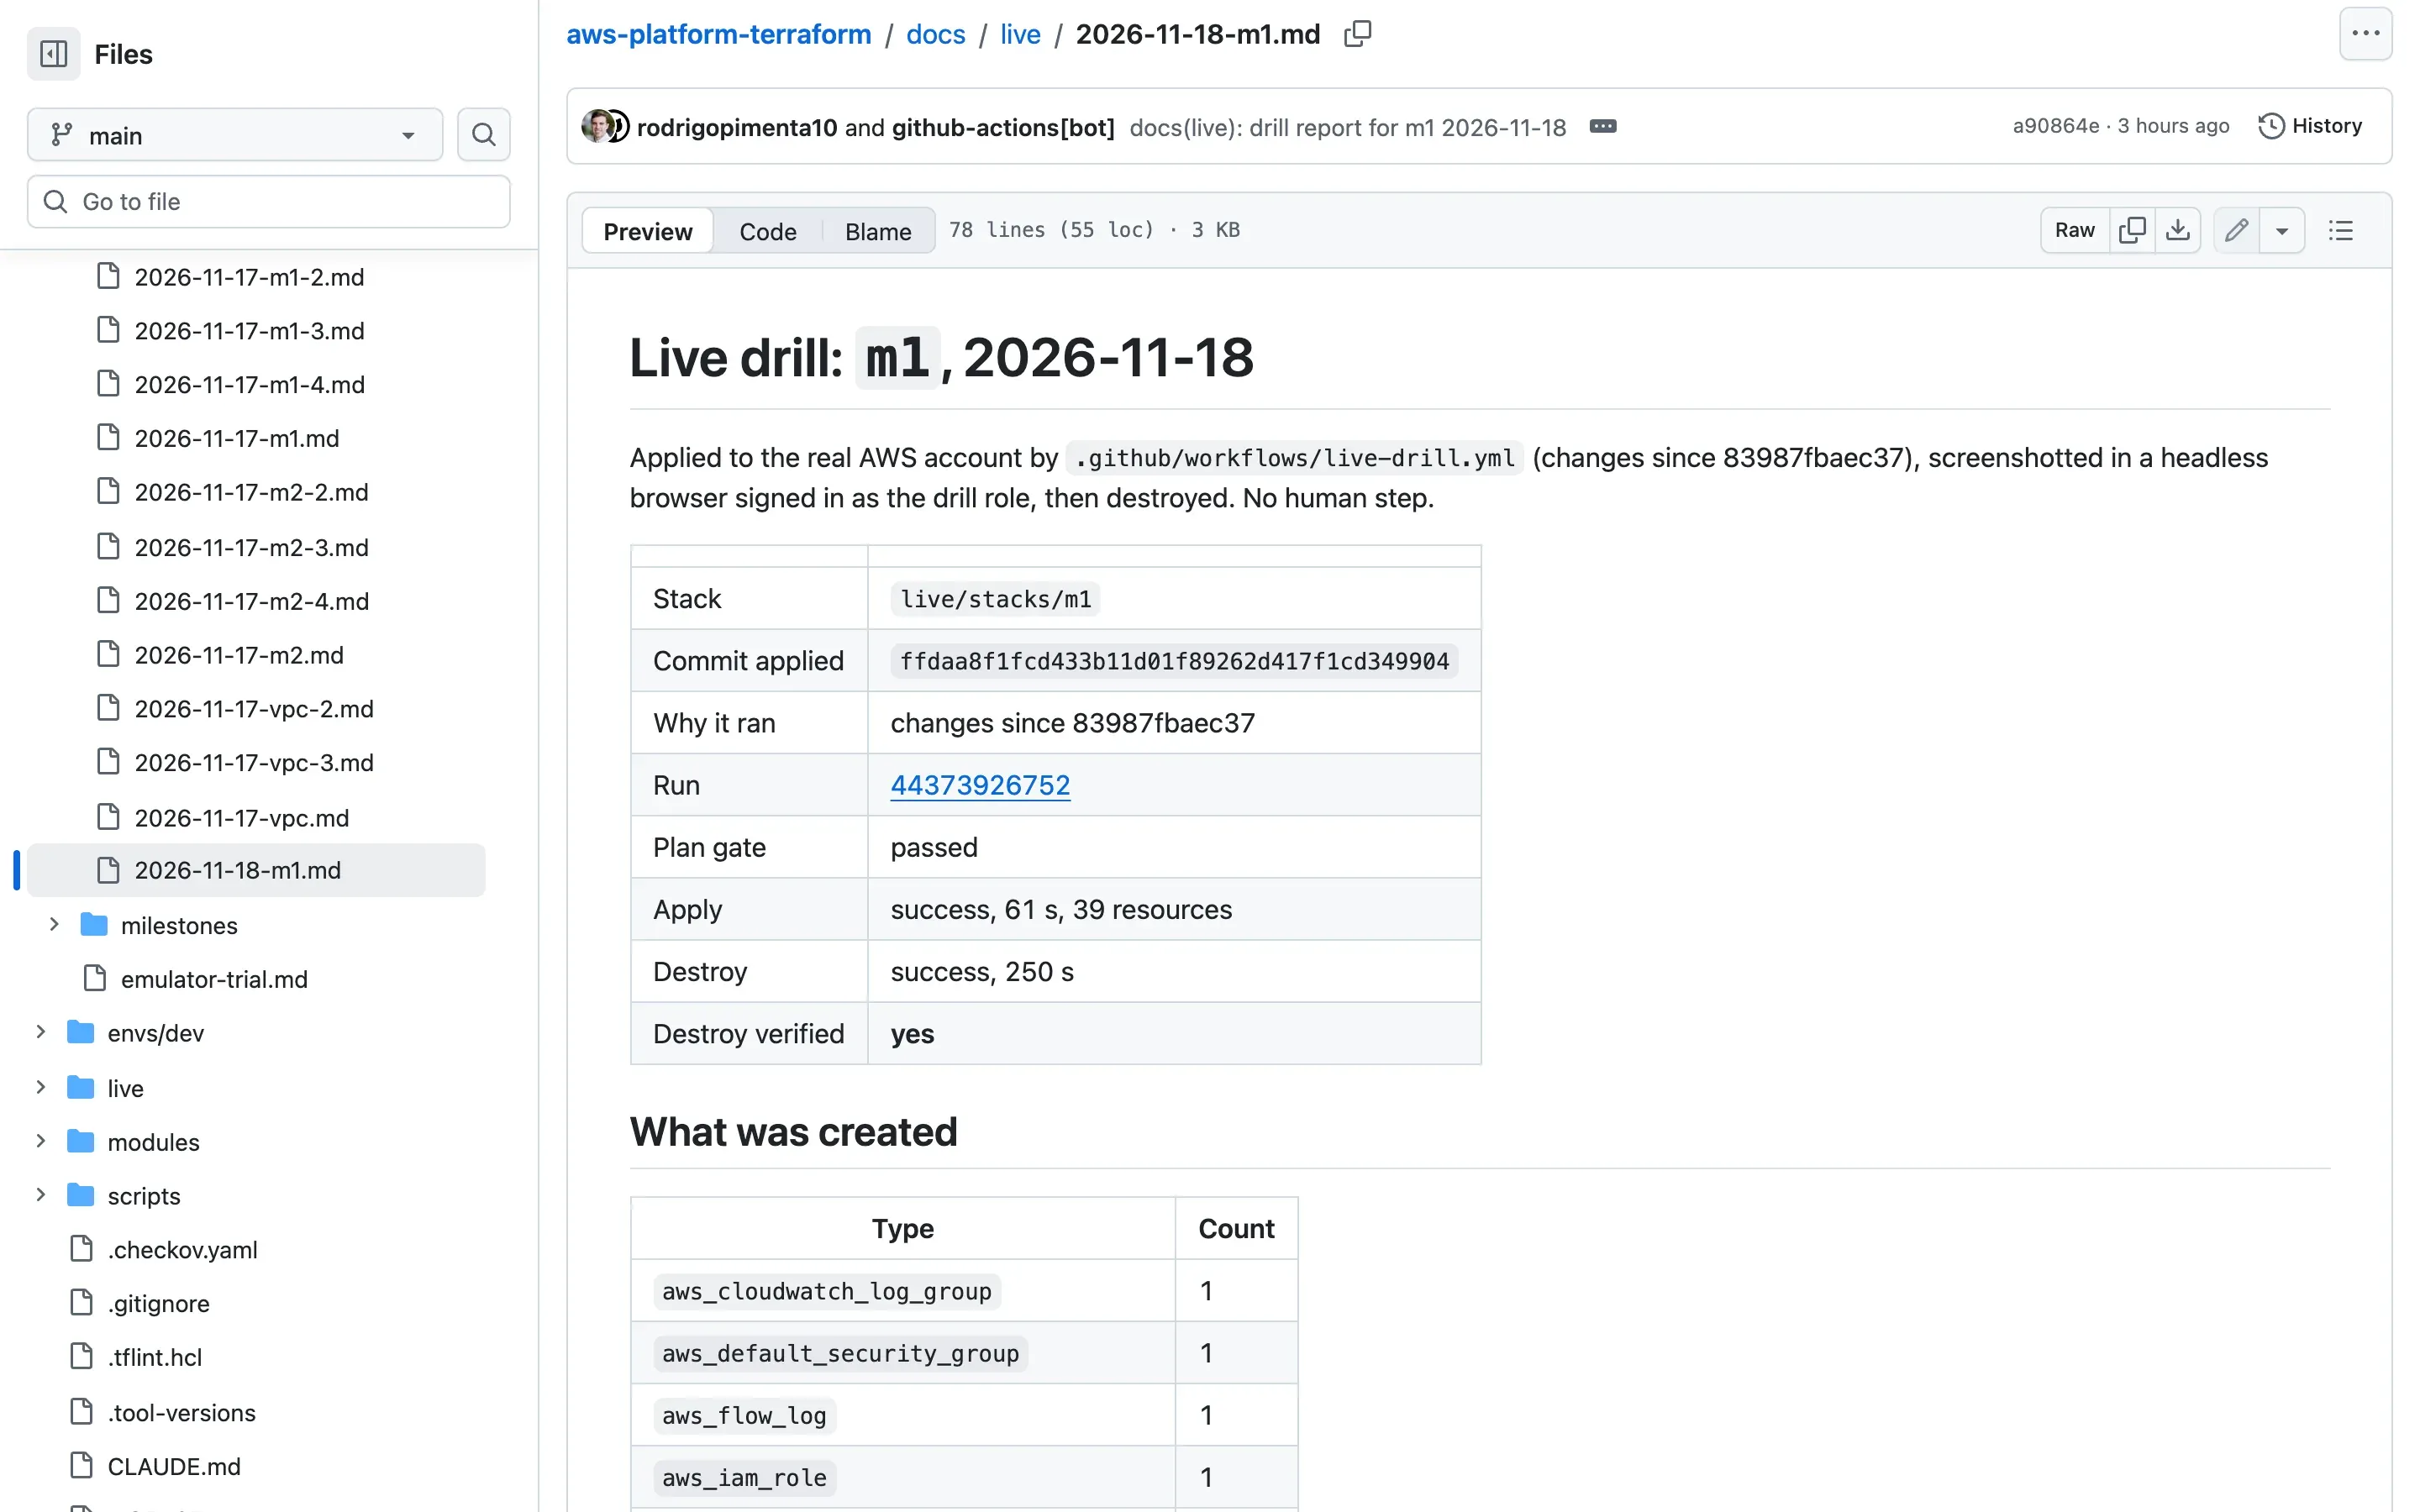
- Every module is tested offline, with no AWS account. GitHub Actions then applies the live stacks to a real account through OIDC, with no stored keys, and destroys them again. More than 20 drill reports with redacted console screenshots are in the repo.
- Stack
-
- Terraform
- terraform test with mock providers
- Moto
- tflint
- checkov
- GitHub Actions with OIDC
What it is
Networking, identity, containers, serverless, observability and CI/CD on AWS, written as reusable Terraform modules with tests. Done so far: remote state, VPC, VPC endpoints, flow logs, KMS, GitHub OIDC and IAM permissions boundaries. EKS, serverless and observability are on the roadmap.
How it is built
I am building it with Claude Code as a structured way to learn AWS platform engineering. A scheduled run takes the next item from the roadmap, builds it with tests and pushes it once every check passes. It also writes a learning note: what was built, why, the trade-offs, an exercise and interview-style questions. I review what it built and study the note. Commits written by Claude say so in a trailer.
How it is tested
Every module has terraform test files of two kinds: unit tests with a mocked AWS provider and
no network, and integration tests that really create and destroy resources against Moto, a local
AWS emulator. CI also runs terraform fmt, validate, tflint and checkov. None of that
touches a real AWS account. The unit tests also pass under OpenTofu.
Live drills
Tests prove the code; a live drill proves it works in a real account. After CI passes on a push
to main, a workflow applies every stack whose files changed since the last successful drill. It
assumes its AWS role through GitHub OIDC, so no AWS keys are stored anywhere. It saves read-only
evidence and console screenshots with the account ID redacted, destroys the stack, checks that
nothing is left, and commits a report.
The drill runs inside limits it cannot loosen: a plan gate refuses forbidden resource types, the role is boxed in by IAM denies and a permissions boundary, a budget action cuts it off at the spend limit, and a separate reaper workflow destroys anything a drill leaves behind.
The row for this project on the home page is the latest of those drills, read from GitHub’s public API.
Architecture · scroll sideways for all of it →
Where these claims come from
-
A production-style AWS platform in Terraform; a daily Claude Code run builds the next roadmap item, and I review it and study the note it writes.
GitHub profile README and the repository README, "How this repo is built".
-
Every module is tested offline; GitHub Actions applies the live stacks through OIDC with no stored keys and destroys them again.
GitHub profile README; the repository's live-drill workflow.
-
More than 20 drill reports with redacted console screenshots.
Counted in the repository's docs/live/ on 18 November 2026 (23 reports).
-
The unit tests also pass under OpenTofu.
-
Done so far, remote state, VPC, VPC endpoints, flow logs, KMS, GitHub OIDC and IAM permissions boundaries.
GitHub profile README; the modules/ directory of the repository.